Visualizing Data Lineage and Governance
- 30/10/2026
- Posted by: A Gable
- Category: Solution Architecture & Design
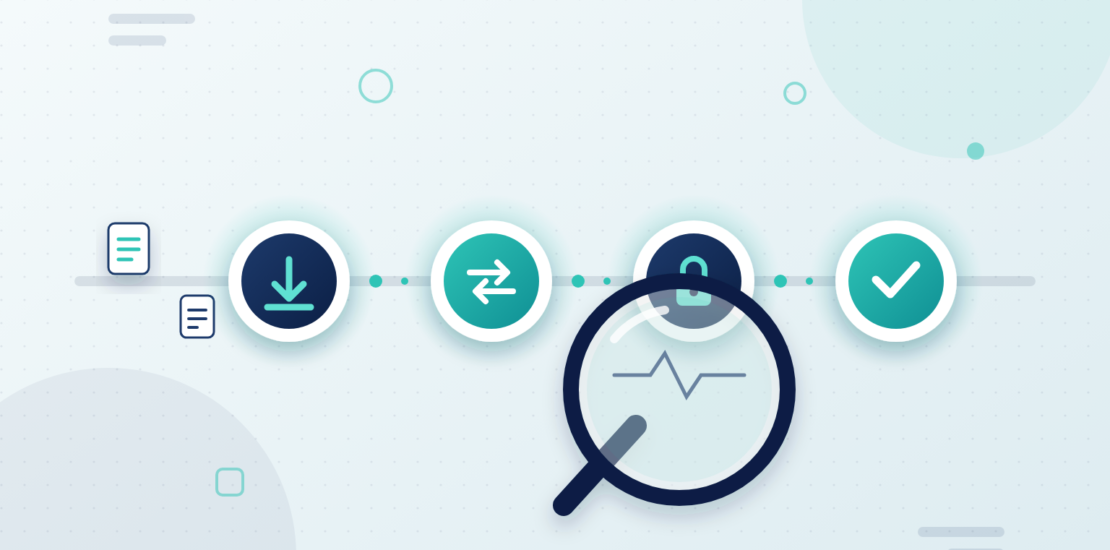
A compliance architect asks, “Can you show me where a customer’s national ID goes after it enters the system, and who can see it?” If you answer with a boxes-and-arrows diagram, you have described data lineage in theory, not proved governance in practice. Regulated buyers want to follow one record, step by step.
Follow one record end to end
Pick a single sensitive record and trace it through four stages, narrating each: ingest, transform, mask and audit. A concrete record beats a generic diagram, because reviewers can check it against their own policies.
- Ingest: where it enters, who authenticated it, what is logged.
- Transform: which fields change, and where the original is stored.
- Mask: who sees the masked value and who can request the clear value.
- Audit: the log entry that proves each step happened.
Show the audit trail, not just the flow
End by opening the log and finding the record’s history in under a minute. Governance claims are only credible when the evidence is retrievable on demand, so rehearse this lookup.
Match depth to the audience
For a security review, expect questions on retention and key management. For an executive, reduce it to one sentence: “Every handling step is recorded and only named roles see the real value.” For a reliability team, add what happens if the masking step fails.
Decision and check
Decision: build one reusable walkthrough around a realistic but fake sensitive record, with a saved audit query ready to run. Check: can a reviewer who did not attend reconstruct the record’s path from your notes and the log alone? If yes, the data lineage story is strong enough for a security questionnaire. If not, add the missing stage.
SE Ignite’s free curriculum teaches vendor-neutral walkthroughs like this one, grounded in the 80% of solution engineering that does not depend on any single platform.